Spring Boot version upgrades—whether moving from 2.x to 3.x, 3.x to 4.x, or even minor bumps like 3.2.5 to 3.3.1—regularly introduce subtle, breaking changes that unit and integration tests miss. JSON serialization shifts, autoconfiguration reordering, and transitive dependency conflicts can silently alter your API contract.
The ability to push an update directly to your users’ devices without App Store review, without delay, without any action required from the user, is one of the most powerful capabilities available to a React Native team. Over-the-air (OTA) updates change how fast you can respond to bugs, iterate on features, and ship improvements. But that power cuts both ways. A bad OTA update reaching 100% of your users at once is considerably worse than a bad store release.
Software engineering teams are operating in environments that look very different from just a few years ago. Modern development workflows now span Kubernetes clusters, cloud infrastructure, CI/CD pipelines, AI-assisted coding, distributed architectures, internal developer portals, observability platforms, and dozens of engineering tools that all need to work together without slowing delivery velocity.
The rise of AI-assisted coding has transformed how software is built. With tools generating entire features in seconds, the bottleneck is no longer writing code—it’s verifying it. Because AI can generate boilerplate and handle API integrations instantly, more service changes are being pushed into authentication logic, API calls, and configurations. Teams desperately need a way to verify these changes before merging, especially when the code touches external dependencies.
AI can write a feature in seconds, but where are you testing it? Sending production traffic, API payloads, and auth headers to a third-party SaaS is a massive security risk. In this video, we break down why the Bring Your Own Cloud (BYOC) model is the ultimate fix for DevSecOps. Learn how to safely test AI-generated code against real production traffic entirely within your own VPC or Kubernetes cluster. No data leaks, no massive DLP pipelines, and no endless masking rules.
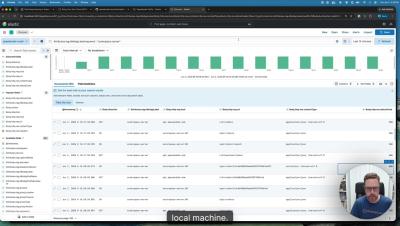
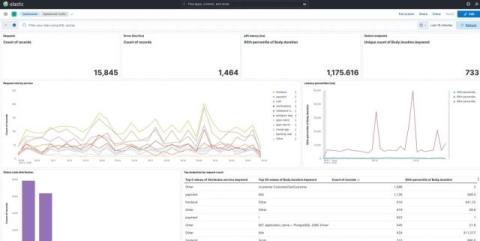
Your logs showed 500 errors. The traces showed the dependency graph. Neither showed the actual bug, a DEL control character getting appended to the query string. This is how I found it. In this video I walk through Speedscale BYOC (bring your own cloud): capture real production traffic, store it in your own Elasticsearch cluster inside your VPC, pull it down locally with a single script, and reproduce the exact bug using proxymock. The data never leaves your environment.
Here’s a problem I run into constantly: something breaks in production, I can see the 500 errors in my logs, but I can’t reproduce it locally. The trace shows me the dependency graph but not the actual request that failed. This is especially painful in microservices. I was looking at a CNCF example the other day (a simple demo app, like 4 pods) and it already had so many cross-service dependencies that understanding what broke required looking at the whole system at once.
Everyone wants an AI agent factory in 2026. Autonomous agents fixing bugs and shipping features while you sleep. I’ve been building toward that myself. But the error rates don’t support the fantasy. The best AI coding agents in the world fix about 50% of real bugs on SWE-bench verified. Half the time they fail. And AI-generated code produces 1.7x more issues than human-written code.