Systems | Development | Analytics | API | Testing

gRPC Mocks, Tests and Contract Checks From a .proto

Change one field in a.proto from double to string, and nothing complains. The code compiles, the deploy goes green, and a service still built from the old contract keeps answering with a double. Here’s what Go’s protobuf runtime does when a client on the new contract reads that answer: No error. risk_score comes back empty, and the nine bytes of the double are tucked away as unknown fields.
iPhone Duo Is Here: What Testing Teams Need to Know

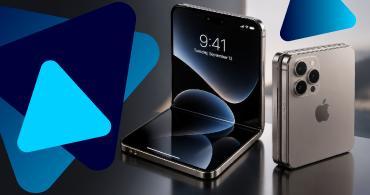
Apple’s first foldable iPhone is here. Your applications need to be ready for a screen that opens, closes, and runs two apps side by side. Perfecto has a long record of supporting new Apple releases, and the iPhone Duo continues it. In this post, you’ll learn what the iPhone Duo means for your testing strategy, how Perfecto helps your team test on it, and how Perforce Autonomous Testing keeps your tests working as devices change. Request Demo Back to top.

New Forrester study: Why modernizing data streaming is about more than cost savings

A new Forrester Total Economic Impact (TEI) study commissioned by Confluent, an IBM company and data streaming platform, found that a representative composite organization achieved 137% ROI, USD 2.1 million in net present value and a 10-month payback period. Those are meaningful results. The ROI is notable. What's more interesting is where the value came from. Modernization is often framed as an infrastructure problem. Leaders compare platform costs, migration and operating costs.

Spotter Is Now Available in Slack and Microsoft Teams

Let’s say a regional sales director posts a soft renewal number in the channel. A teammate asks the question that decides the plan: trend, or seasonal blip? Nobody in the thread can answer, so the thread does what threads do. It moves on, and the plan gets anchored to the most confident opinion in the room. The maddening part: the data existed. It was modeled, governed, correct, sitting in the warehouse the whole time. It's not a data problem; the answer was there.

7 Best Cloud Computer Environments for Autonomous AI Agents

An AI agent can understand a request perfectly and still fail to complete it. The browser loses its authenticated session. A downloaded file disappears when the environment closes. A website presents an unexpected dialog. Two tasks accidentally share the same account state. These failures happen in the execution environment, where an agent's decisions become actions.

OctoPerf 18: Test as Code With K6, and Core Web Vitals for Playwright

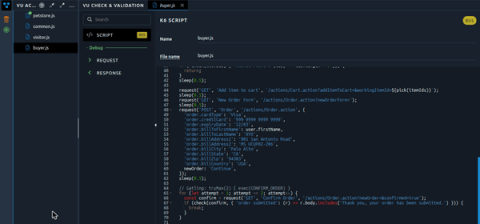
OctoPerf 18.0.0 is out! In version 17 we separated the injection engine from JMeter, and this release is where it starts to pay off: K6 is now available as a load engine next to JMeter and Playwright. Playwright Virtual Users also measure the Core Web Vitals of every page they open. K6 scripts are code, so they usually live in Git next to the application and get reviewed like it. With OctoPerf 18 you can run them without modifying them: This is why we did all that work in OctoPerf 17.

Migrating Gatling Simulations to OctoPerf With an AI Agent

Migrating a load testing project is rarely difficult, but it takes time and it's easy to give up halfway. That's why OctoPerf 18 comes with a Gatling migration playbook for AI agents. In our NeoLoad and LoadRunner walkthroughs, the projects were converted into JMeter Virtual Users. A Gatling simulation is code, so here it stays code: the agent rewrites it as a K6 script, and its injection profile becomes an OctoPerf scenario.

5 Questions to Ask Before the Next Cloud Outage

On October 20, a power failure in one of Google Cloud’s three London zones disrupted Revolut, Lloyds, HSBC and others for hours. One zone failed, errors spread region-wide, and Google warned customers they might not be able to create new workloads to fail over to. Most teams find out how resilient they are during an outage, not before one. These five questions let you find out first.

The Security Domino Effect: Why Trust Can't Be an Afterthought in AI

In interconnected software environments, a security vulnerability rarely exists in isolation. A weakness in one component can expose credentials, create unintended access paths, or give attackers a foothold in connected services. The consequences depend on what that component can access, the permissions it holds, and the safeguards around it. As organizations adopt cloud platforms, third-party integrations, and AI-powered development tools, the boundaries between systems matter more than ever.